
Its options are built to address hybrid environments, compliance calls for, and preparation for post-quantum cryptography (PQC). Institutions will face transitional phases the place classical and quantum-safe algorithms should coexist. Options must be designed to manage this complexity without compromising performance or security.
Without operational security and continuous evidence, offers stall—especially for cloud providers dealing with regulated information. ISO is probably one of the most trusted security frameworks for demonstrating that a company operates an data safety management system (ISMS). A recurring theme across the newest ISO key administration best practices is the necessity for strong cryptographic controls to protect knowledge confidentiality, integrity and availability.

Unlock Cloud Safety Insights
In Hardware Security Modules, secure enclaves or encrypted key stores — protected towards unauthorised access, extraction and tampering. Ideally the secret’s generated inside that boundary and never leaves it, so there is not any window in which it exists within the clear. Knowledge spread throughout AWS, Azure, Google Cloud and your individual data centres is protected by keys in a quantity of completely different key providers. Key Lifecycle Management is the end-to-end governance of a cryptographic key, from era to destruction. Take the subsequent step HSM-as-a-Service automates generation, rotation, and verifiable destruction throughout your whole key estate.
What’s A Private Ca? When To Run Your Own Certificate Authority
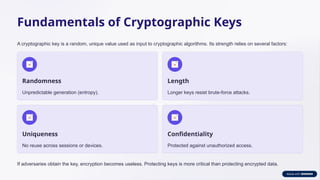
Hardware Safety Modules (HSMs) deal with cryptographic operations within a safe hardware boundary, ensuring that keys by no means go away the protected reminiscence. Key utilization ensures the operational availability of keying materials through the applicable crypto period of the keys. Depending on the kind of key institution protocols, the key could also be short-term (session key) and need revocation on the expiration finish of the digital certificate. Once an encryption algorithm (such as RSA, ECC, or AES) is selected, both key size and randomness play a crucial position in guaranteeing information stays protected in opposition to evolving cyber threats. AI can help detect suspicious patterns, automate threat responses, and suggest key rotation schedules.
Cloud-native purposes often handle encryption internally utilizing service-level encryption. Without centralized oversight, this results in fragmented key visibility and governance, rising the chance of mismanagement or key publicity. The rise of quantum computing represents one of the most profound shifts in cybersecurity. Though absolutely succesful quantum computers https://compitionpoint.com/secure-your-oracle-apps-with-best-practices/ have not yet materialized, the „Harvest Now, Decrypt Later“ risk model is already energetic.
- Servers, service meshes, IoT units and connected vehicles every maintain a private key behind their certificates — the id Zero Belief is determined by.
- Enterprise encryption key administration techniques (KMS) are options designed to manage, retailer, and defend cryptographic keys throughout entire organizational cryptographic environments.
- Efficient key administration underpins confidentiality (only authorised events can decrypt data), integrity (modifications are detectable) and authenticity (the id of the sender or signer is verified).
- Encryption serves as a critical line of protection, safeguarding info by rendering it unreadable without a decryption key.
More Iso 27001 Guides
This centralization reduces complexity, strengthens compliance, and improves response instances to breaches or audits. The ongoing migration to cloud and hybrid-cloud architectures reshapes how encryption keys are dealt with. Decentralization, dynamic scaling, and data locality requirements introduce new challenges for constant key administration.
Nist Standardization
Digital encryption key administration addresses these considerations, ensuring that keys are correctly generated, distributed, saved, and rotated to maintain up their security over time. Book a demo and we’ll show how Konfirmity evidences your key technology, storage, rotation and revocation practices across cloud KMS and the legacy methods auditors all the time probe. Key vaults can enhance safe storage through enhanced access management together with encryption at rest.